
Author: Nishtha Mehrotra | EQMint
Synopsis:
-
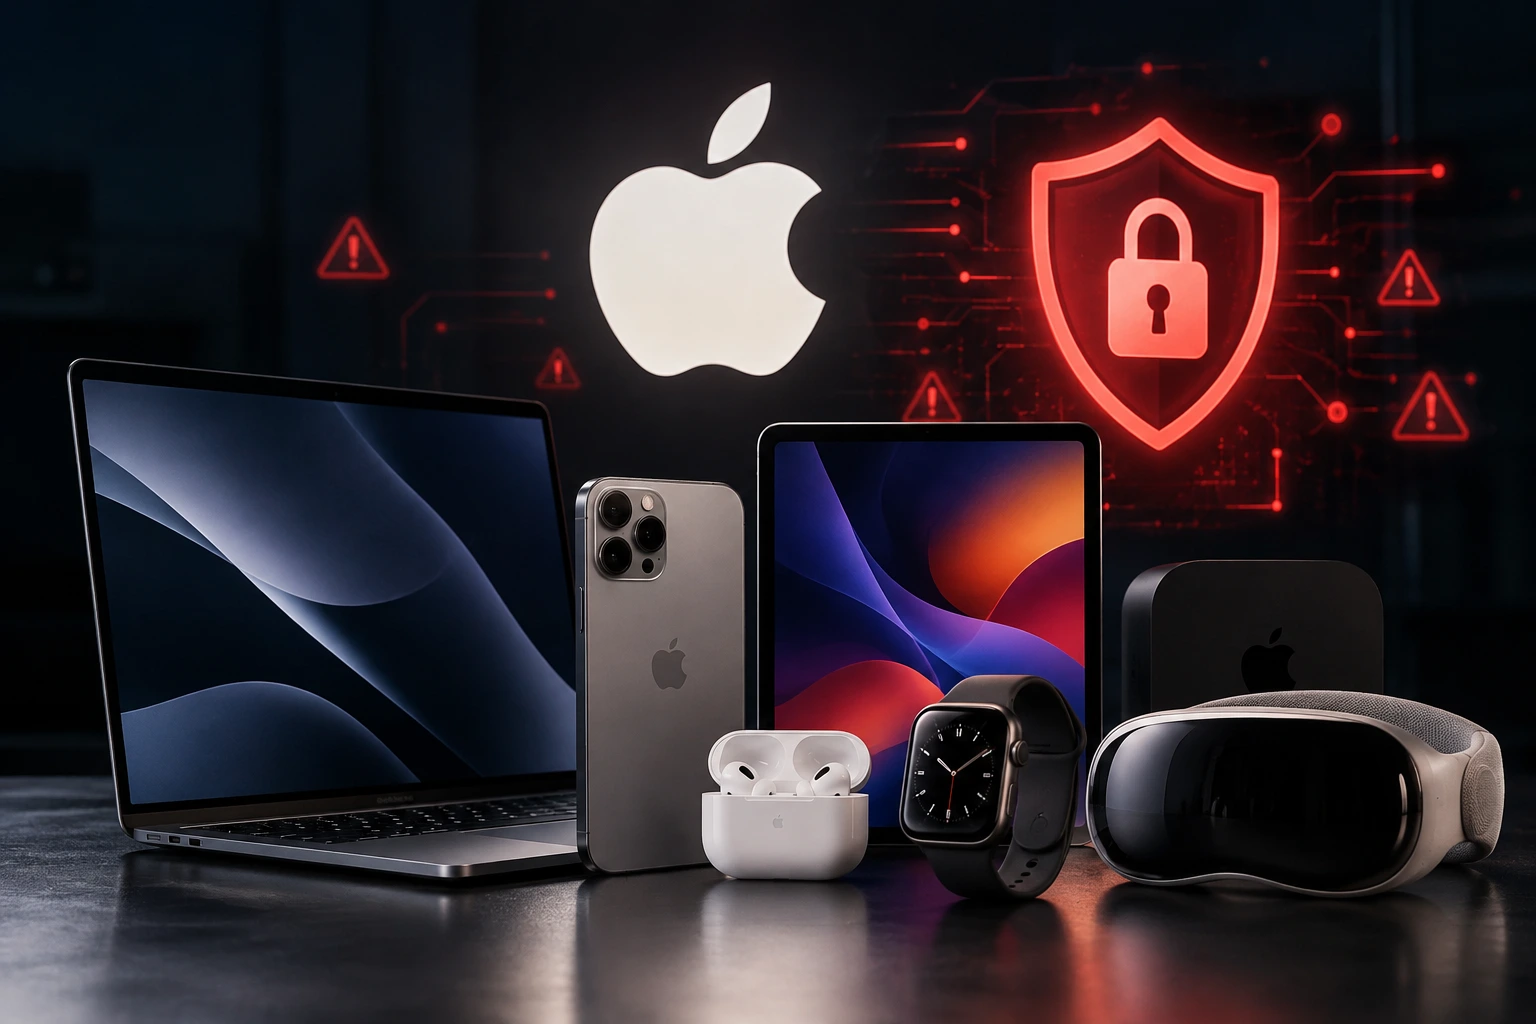
- CERT-In issued a high-severity warning covering vulnerabilities across Apple’s iPhones, iPads, Macs, Apple Watches and other devices.
-
- The flaws could allow attackers to execute malicious code, access sensitive information or bypass security protections.
-
- Users should install the latest compatible software updates and enable automatic updates to reduce their exposure.
India’s cybersecurity agency CERT-In has issued a high-severity warning for multiple Apple products, flagging software vulnerabilities that could expose users to cyberattacks.
The advisory, published on 28 October 2026, covers several Apple operating systems and products, including iOS, iPadOS, macOS, watchOS, tvOS, visionOS and Safari.
The identified weaknesses include memory corruption, buffer overflows and security validation errors. Attackers could potentially exploit them through specially crafted web content or files to execute unauthorised code, gain elevated privileges, access sensitive data or disrupt device operations.
The warning applies to users running software versions earlier than the affected products’ specified security updates. Apple has reportedly released patches to address the vulnerabilities.
Users should check for updates immediately. iPhone and iPad users can navigate to Settings > General > Software Update, while Mac users can check System Settings > General > Software Update. Apple Watch and other compatible devices should also be updated to their latest supported versions.
Individuals and organisations should enable automatic updates and avoid opening suspicious links or attachments. Users should verify the exact affected versions against the original CERT-In advisory before publishing or acting on specific version thresholds.
Source: https://shrts.in/numkkysaqw
Disclaimer: This article is for information purposes only and is not investment advice.
For more such information, visit EQMint
Join our WhatsApp channel for timely updates: Whatsapp